

ClickFix attacks are a rising cybersecurity threat in 2026, using fake websites or compromised legitimate sites to trick people into installing malware themselves.
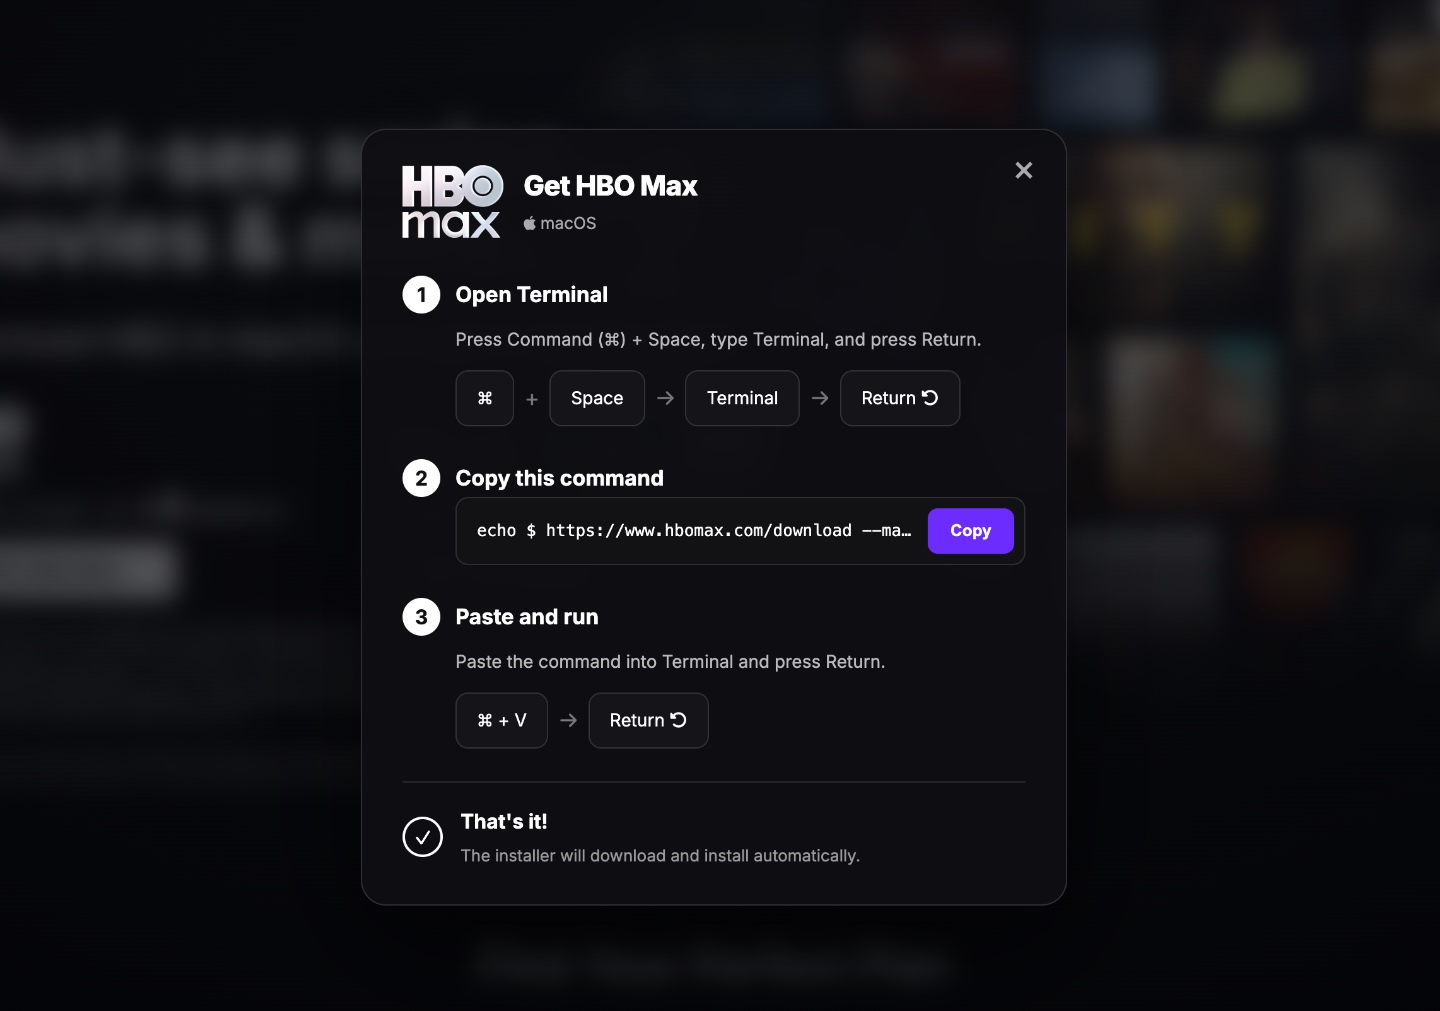
The attacks often show a fake CAPTCHA or anti-bot checkbox. After a user clicks it, the page displays instructions to copy and paste text into Windows Command Prompt or PowerShell, or the Terminal app on macOS. Pressing return can instantly install info-stealing malware that steals passwords, access to logged-in accounts, and crypto wallets.
Because the user is interacting directly with the operating system through terminal commands, the attacks can evade antivirus and other security tools.
Security researchers say the latest campaign used fake Reddit ads linked to pages that resembled HBO Max. Hackers compromised the official HBO Max account on Reddit and used it to post hundreds of realistic-looking adverts, according to Hudson Rock and a thread in Reddit’s cybersecurity subreddit.
It remains unclear how many people clicked the ads or how many were compromised. Warner Brothers Discovery and Reddit did not respond to requests for comment.
Security researcher Kevin Beaumont said companies can block Command Prompt and PowerShell across Windows domains. Ars Technica also noted BlockBlock, a Mac tool designed to defend against attacks that try to trick users into running malicious commands.
Comments
0No comments yet. Be the first to comment.