

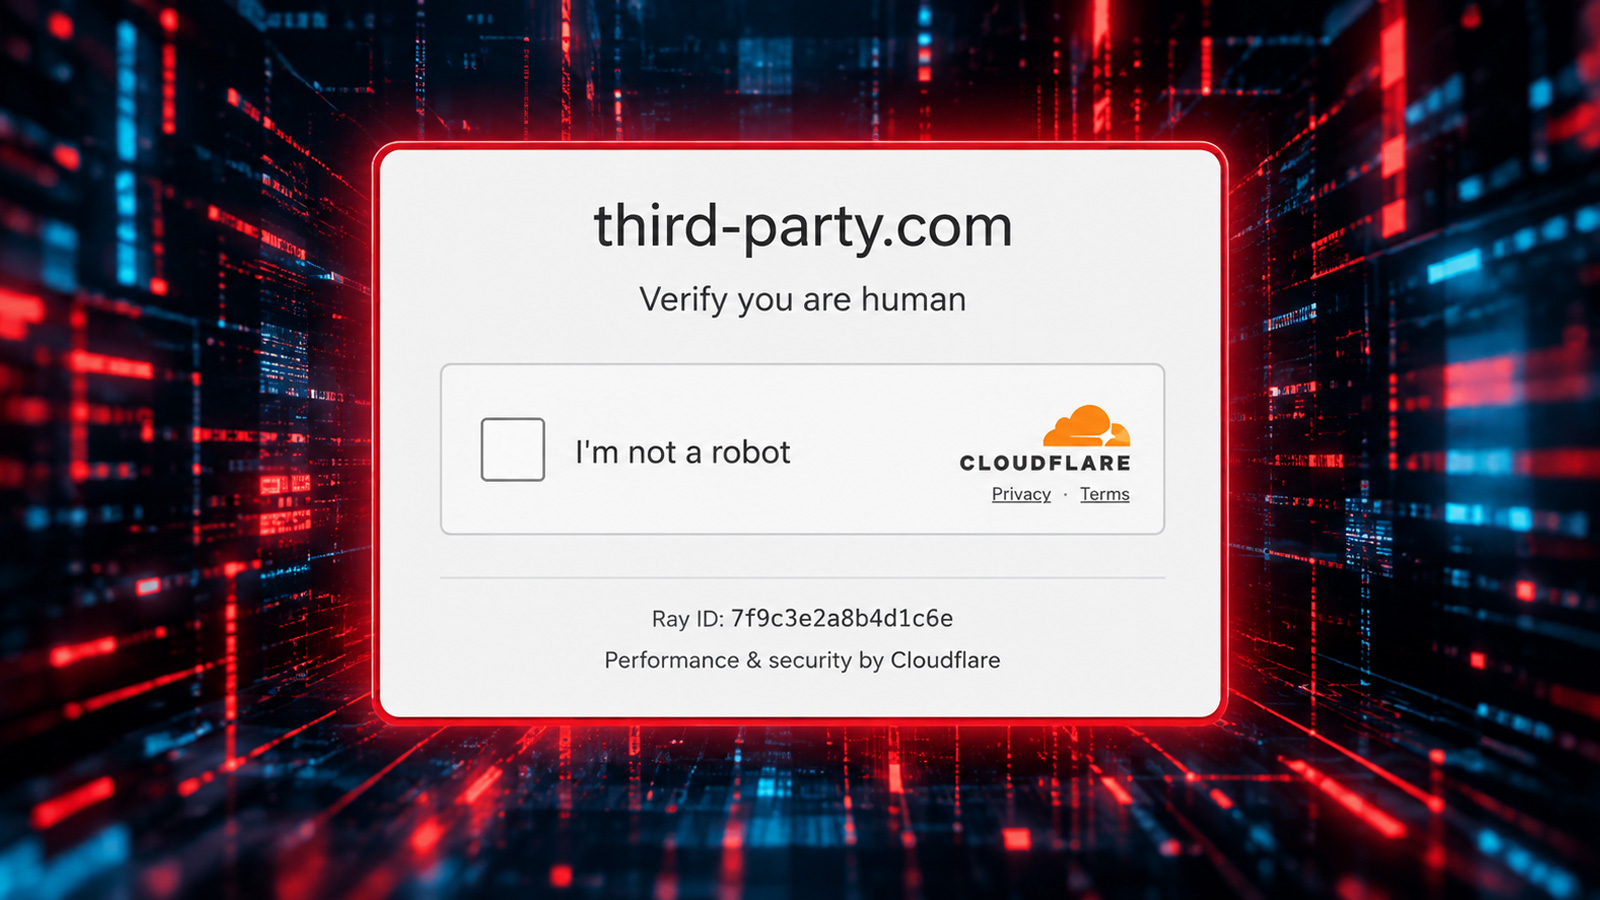
BleepingComputer reports that third-party.com, a domain often used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that targets Windows users with a ClickFix attack.
The page asks visitors to verify that they are human, then copies a malicious PowerShell command to the Windows Clipboard. It instructs users to press Windows key + R, paste the command with Ctrl+V, and press Enter. The command reconstructs a URL, downloads a PowerShell script, and runs it.
At the time of BleepingComputer’s testing, the payload URL no longer resolved. A Hybrid Analysis report dated May 2, 2026, showed that the site had distributed a PowerShell script configured to download a 134MB archive and attempt to launch draw.io.exe. The archive was unavailable, so the payload’s purpose could not be determined.
Manifold Security found the campaign while reviewing public AI skills and MCP server documentation. A code search found third-party.com in more than 1,500 files across 1,700+ repositories, including references associated with Chromium, Sanity, and Vercel. The domain was registered in 1996, and BleepingComputer has not determined when control changed. Manifold said the ClickFix lure had been served since at least June 2026. There are no reports that these references have resulted in executed attacks.
Comments
0No comments yet. Be the first to comment.