

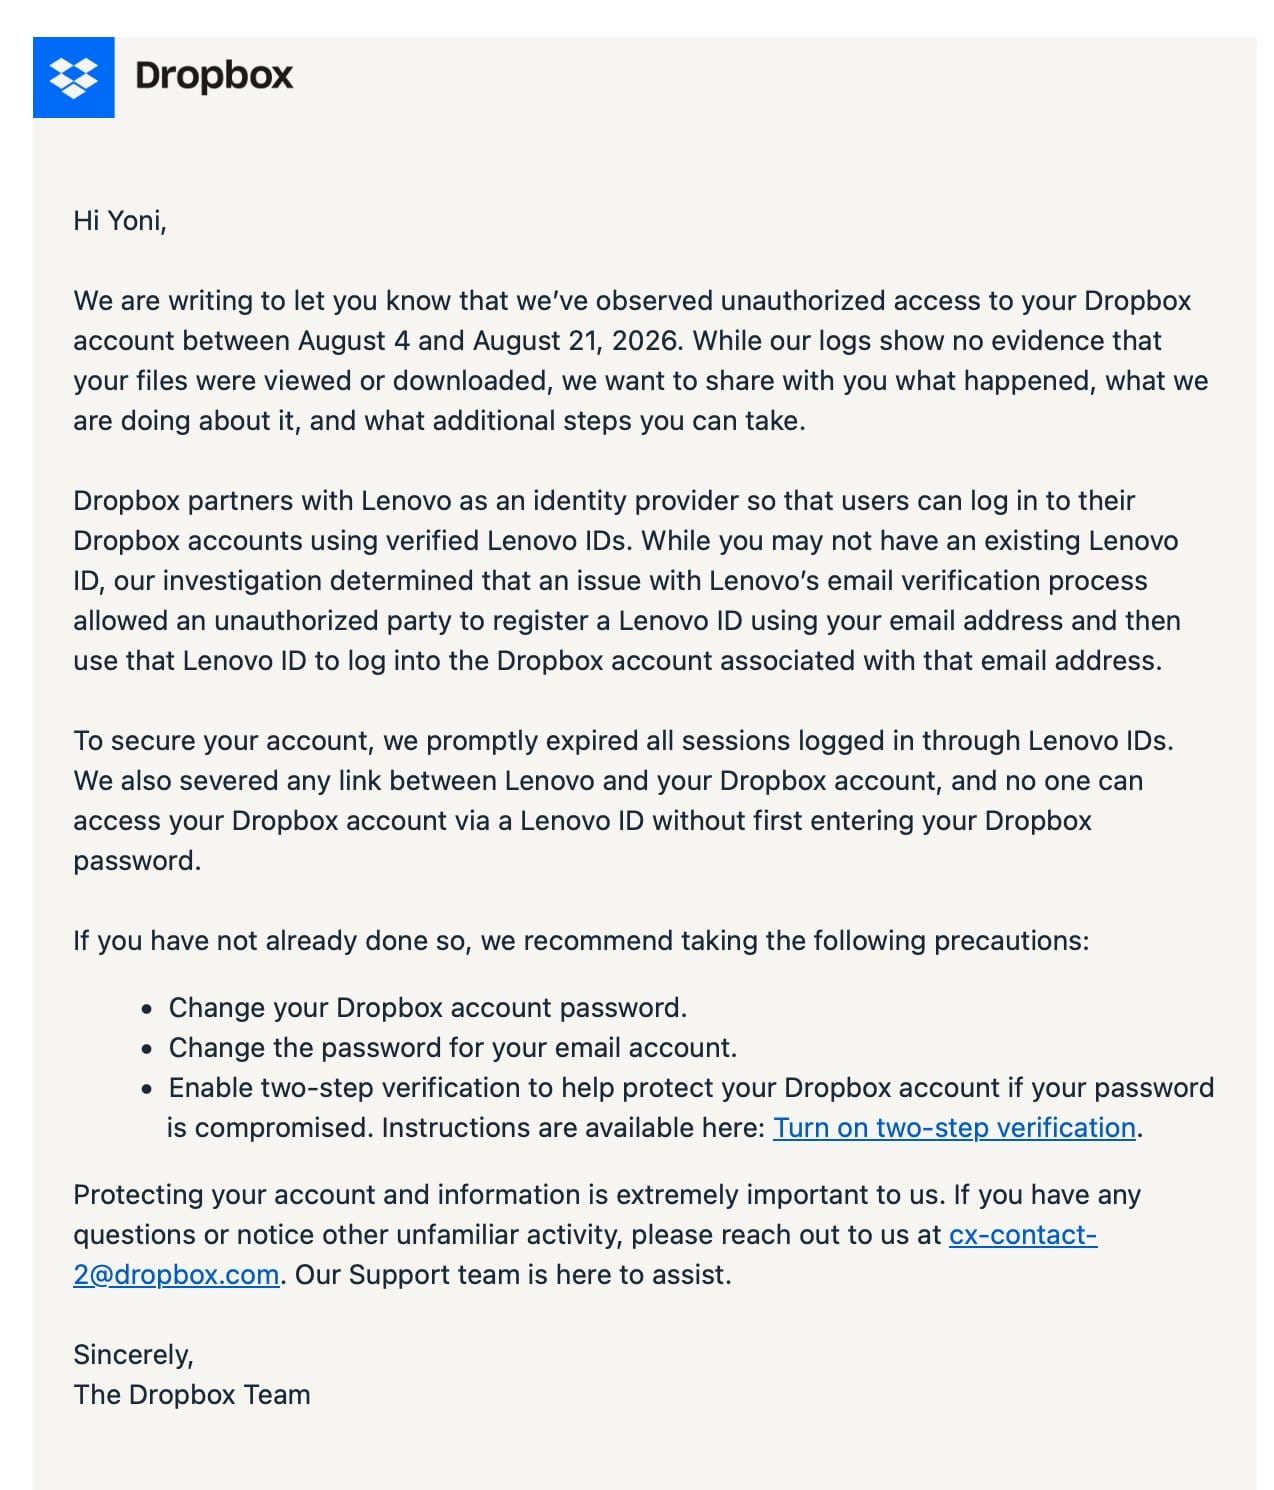
Dropbox warned some users that an unauthorized party accessed their accounts by exploiting an issue in Lenovo’s email verification process.
The flaw allowed the attacker to register a fraudulent Lenovo ID using a user’s email address. The attacker then used that Lenovo ID to access the Dropbox account associated with the same address without entering the Dropbox login password.
Dropbox uses Lenovo Identity Provider Services in its authentication infrastructure, allowing users to sign in with verified Lenovo IDs. Its identity-linking process trusted Lenovo’s assertion that the attacker controlled the email address without requiring confirmation through the existing Dropbox login method.
Dropbox determined that the unauthorized access occurred between August 4 and 21. It said the investigation continues and that it is unclear how many users were affected. The company also determined that Lenovo customers were not affected.
Lenovo said the issue involved a legacy integration between Lenovo ID and Dropbox that could be used to improperly authenticate certain Dropbox accounts. Lenovo and Dropbox worked together to mitigate the risk.
Dropbox expired all sessions authenticated through Lenovo IDs and added a requirement for users to enter their Dropbox account password when using Lenovo ID authentication. Some users had reported suspicious sign-in notifications and an unexpected “Continue with SSO” option.
Comments
0No comments yet. Be the first to comment.