

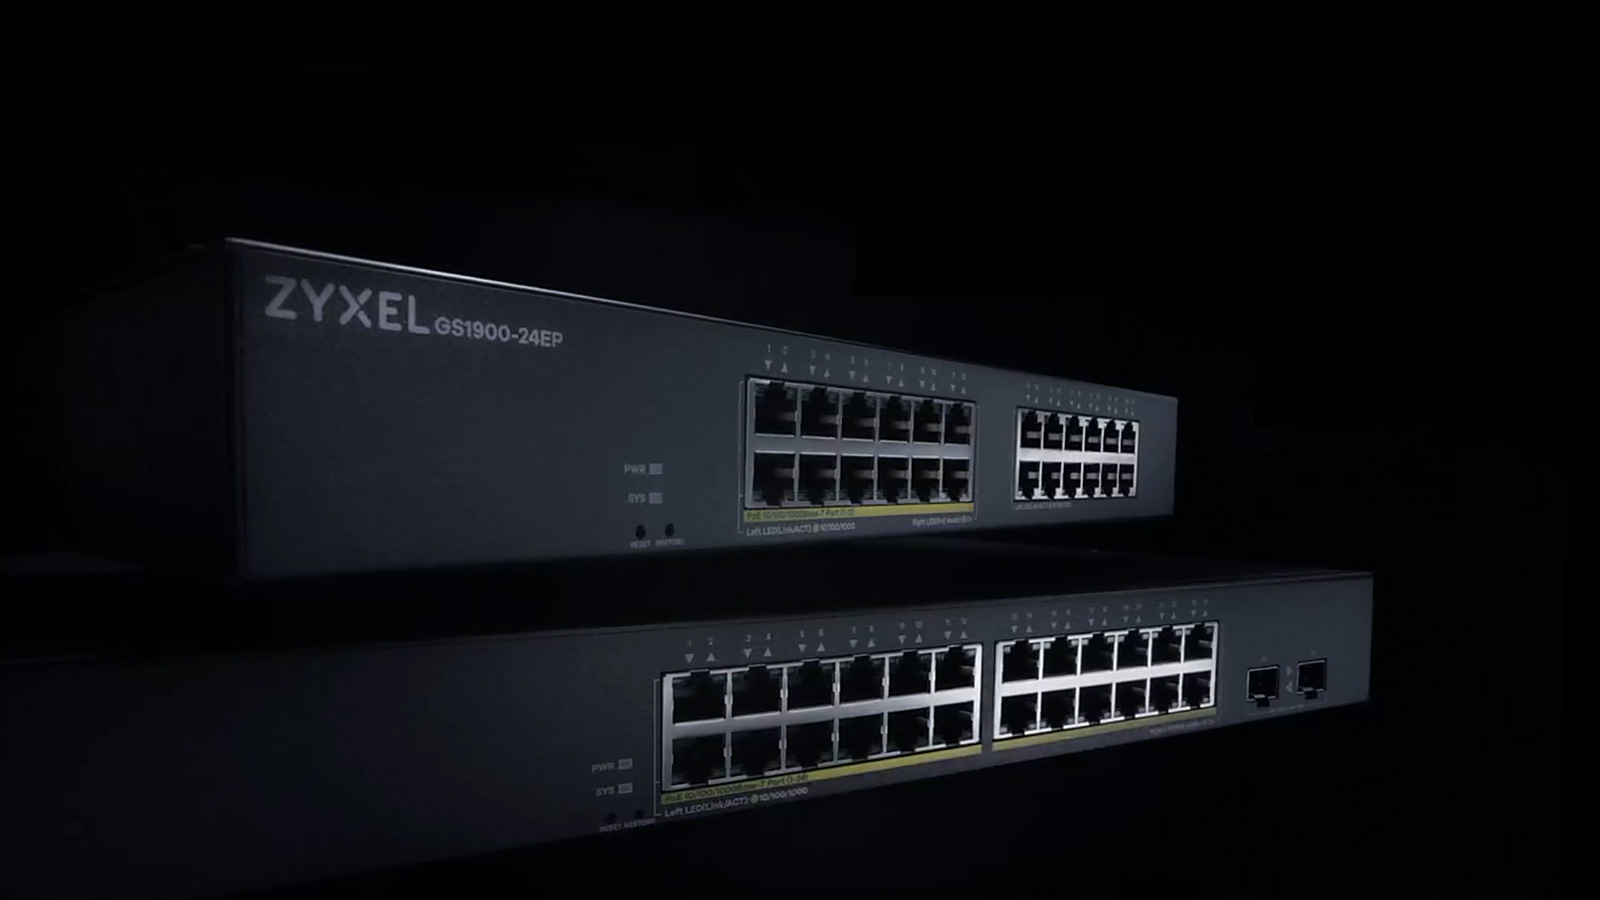
Zyxel has released a security update for a zero-day vulnerability in its GS1900 series network switches after attackers used it to compromise 996 devices across 48 countries, according to cybersecurity company GreyNoise.
Tracked as CVE-2026-107441, the flaw is an out-of-bounds write in the switches’ web management interface. An unauthenticated attacker with network access could send specially crafted HTTP requests to execute operating system commands. The attackers used the flaw to download a script that collected device configurations, hashed root credentials and network information.
Zyxel had released updates in June for a different vulnerability, CVE-2026-7273, affecting the same switches. GreyNoise initially attributed the attacks to that older flaw. Researchers at firmware security company Binarly later found an exploit targeting a separate vulnerability that remained effective even on firmware updated for CVE-2026-7273.
Binarly reported its findings to Zyxel on September 29, and Zyxel confirmed the new vulnerability on October 11. The company released firmware updates on October 22. They limit HTTP parameter sizes and validate the parameter count before copying data into memory. Zyxel published a security advisory on November 3.
GreyNoise observed the suspected Chinese-speaking threat actor Kapibala exploiting the switches starting around August 17. It linked Kapibala to the Red Heron campaign. Whether the recovered exploit was deliberately built to bypass the June updates remains unclear.
Comments
0No comments yet. Be the first to comment.