

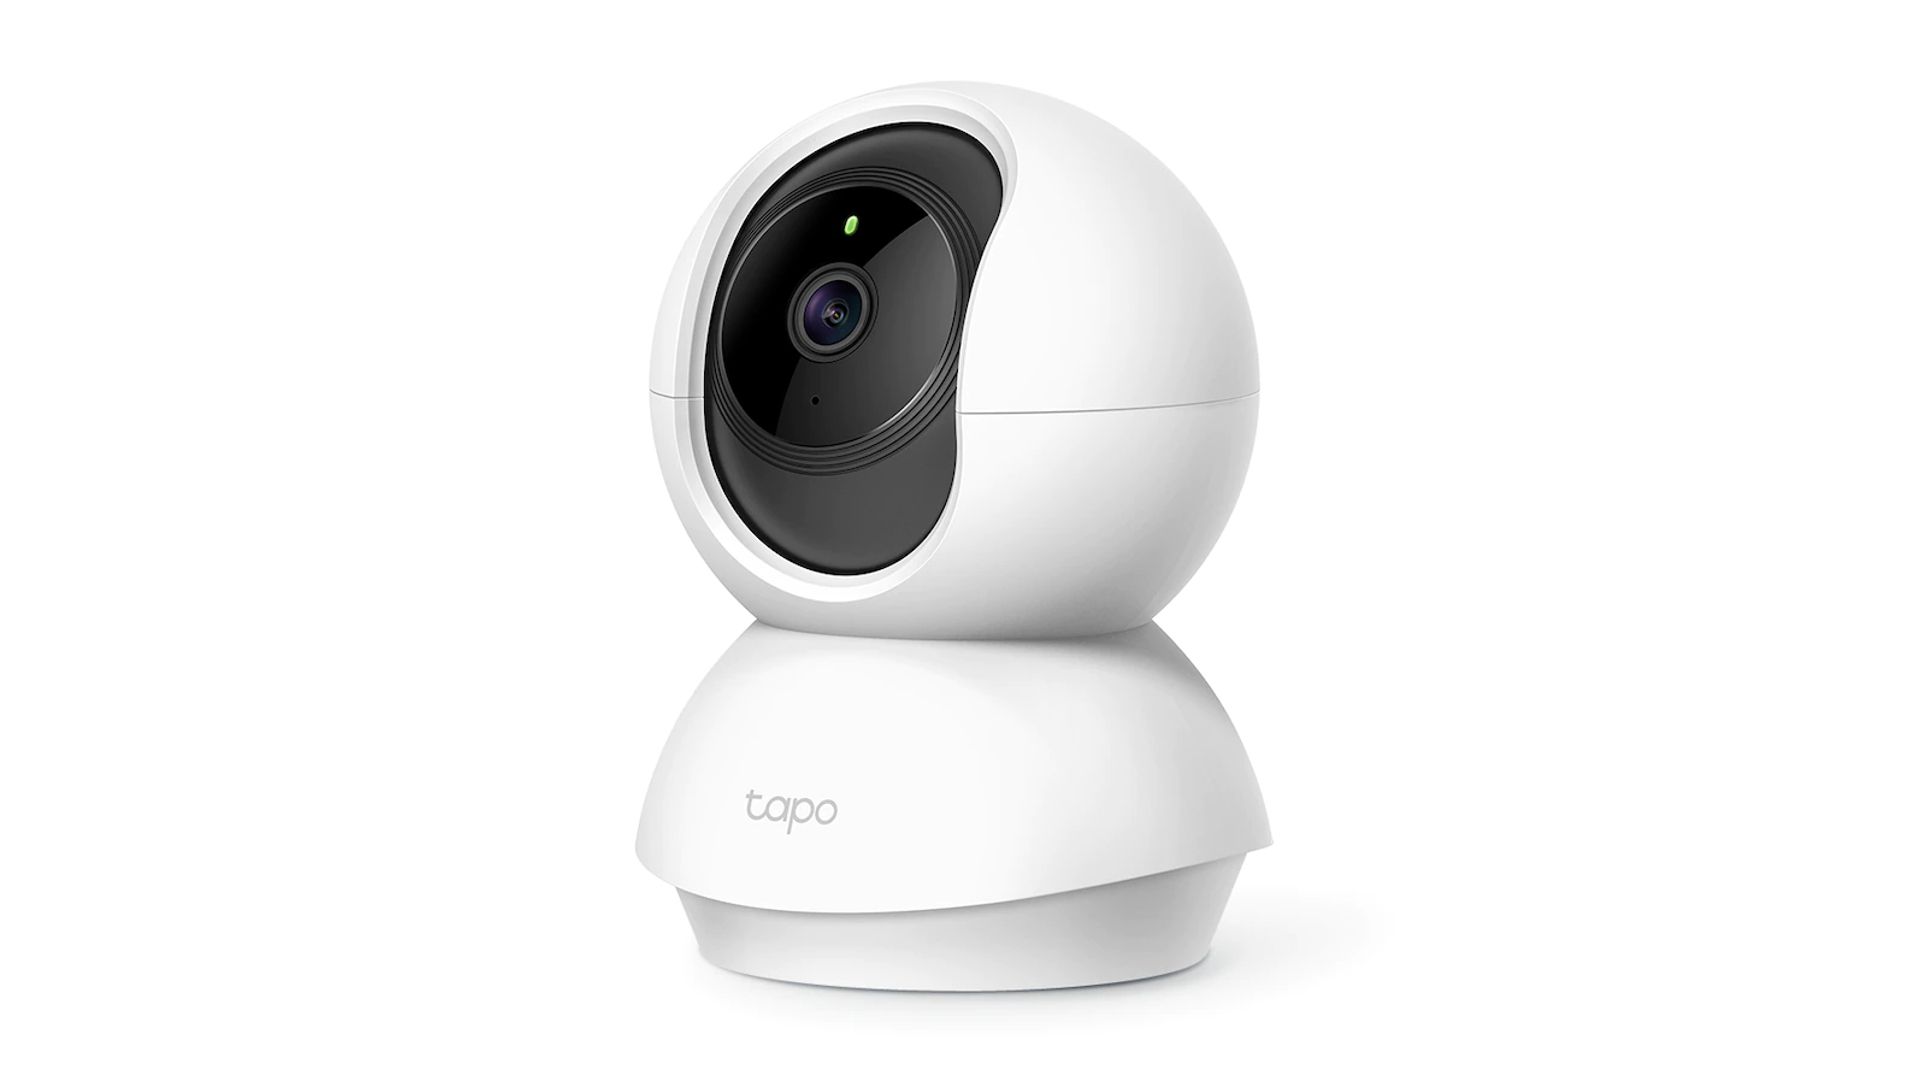
Security researchers have disclosed two vulnerabilities in TP-Link’s Tapo C200 smart security camera. The first, an authentication-bypass flaw tracked as CVE-2026-15315, received a severity score of 8.7/10. Opswat said unauthenticated attackers could obtain valid administrator sessions without a password, allowing them to manage the camera and view its stream.
The second flaw, CVE-2026-15316, received a severity score of 7.1/10. Attackers could send oversized encrypted ciphertext values that may trigger exception-handling failures and cause the device to crash or restart. The NVD said successful exploitation could temporarily disrupt HTTPS management and monitoring until the service recovered.
TP-Link released firmware version V5_1.4.6 on August 18, 2026, addressing both vulnerabilities. Opswat said it disclosed the findings in mid-April, while TP-Link began working on a fix in early July.
The C200 supports 1080p video, two-way audio, night vision, motion detection, cloud and SD card storage, Alexa, and Google Home integrations. The researchers did not say whether the flaws were being exploited in the wild. Dahvid Schloss of Suzu Labs said exploitation requires local network access, although internet exposure through port forwarding would present a greater concern.
Comments
0No comments yet. Be the first to comment.