

A TechRadar investigation found 369 VPN extensions targeting Russian users on Google’s Chrome Web Store that failed basic transparency and professionalism checks. The extensions had more than 218,000 users combined, and over 120 used names associated with legitimate brands.
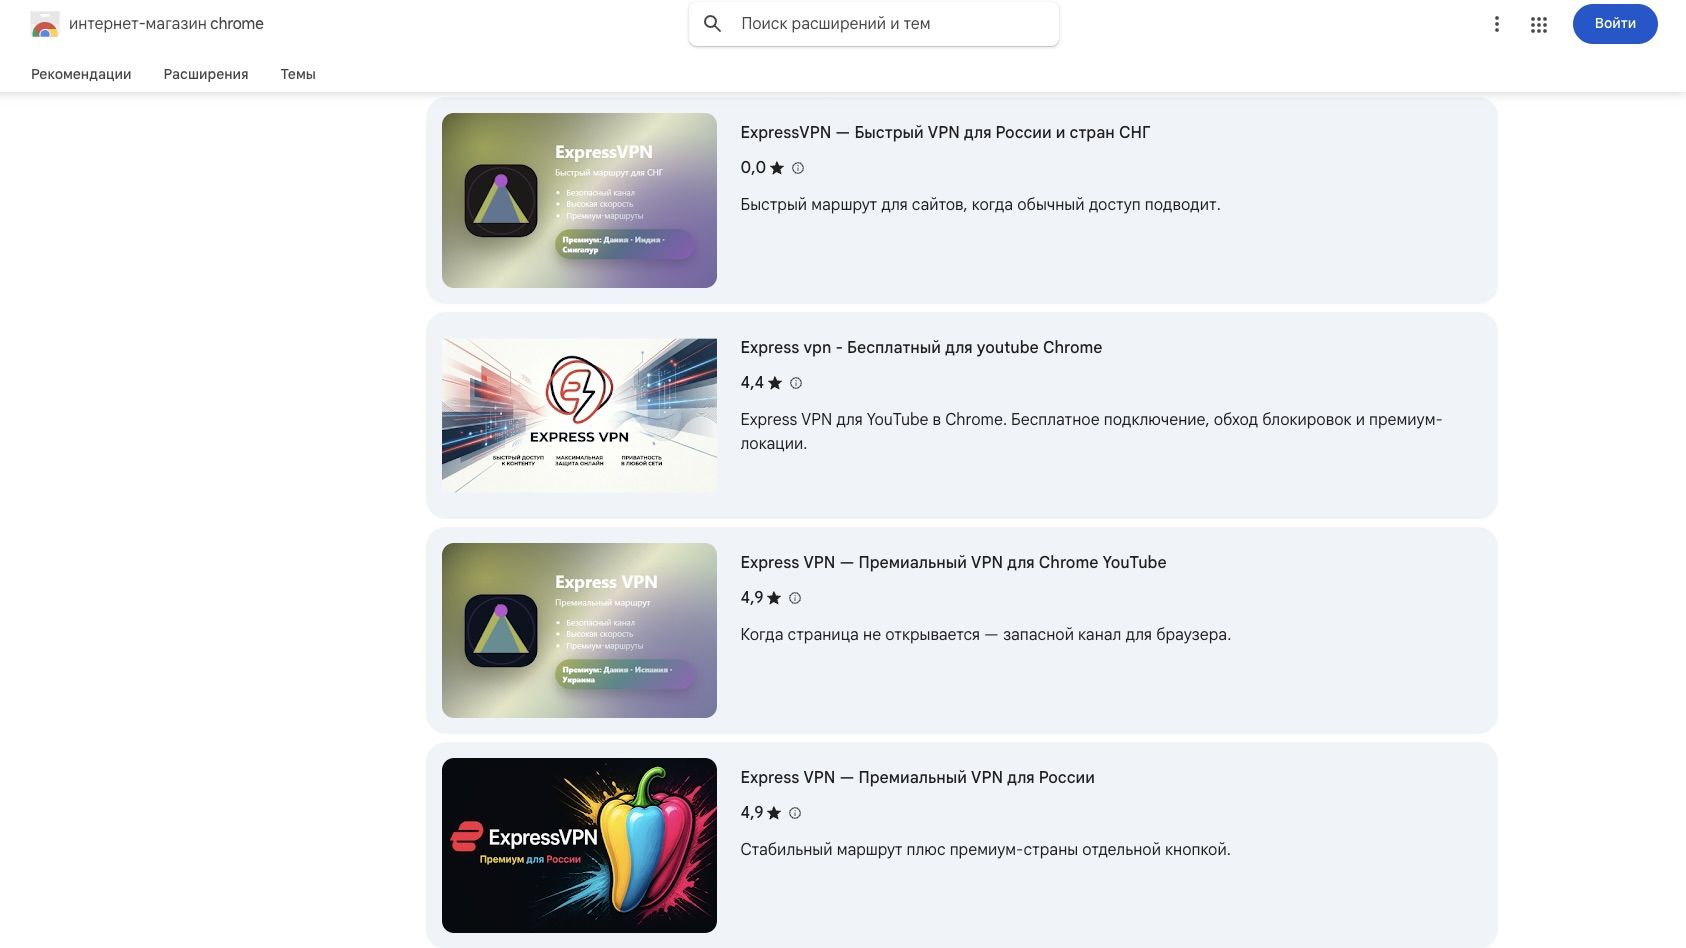
TechRadar found that 70 developers were responsible for the extensions. Nearly three-quarters hosted privacy policies on Telegra.ph, while 47% had more reviews than users—a pattern that may indicate review manipulation. More than 15 extensions used the name Happ, and the investigation identified seven extensions imitating Windscribe and five impersonating ExpressVPN.
Both companies told TechRadar they ask Google to remove copycat extensions when they find them. ExpressVPN’s Head of Security Operations, Cherlynn Cha, said copycats put people at risk by creating a “false sense of security.” Windscribe’s Head of Growth, Rebecca Rosenberg, described removals as a “game of whack-a-mole.”
VPN extensions can access sensitive browsing data because they route a user’s internet connection through their operators’ servers. TechRadar said it could not determine which extensions were harmful without detailed testing. It found that 89 extensions previously flagged by Palo Alto were still available to Russian users. Google had not responded to TechRadar by publication time.
The investigation comes amid restrictions on digital services in Russia following the 2022 full-scale invasion of Ukraine. The source says VPNs have become an important tool for millions of people there, while authorities have moved to regulate and restrict access. It also notes there is no evidence the extensions are linked to Russian authorities.
Comments
0No comments yet. Be the first to comment.