

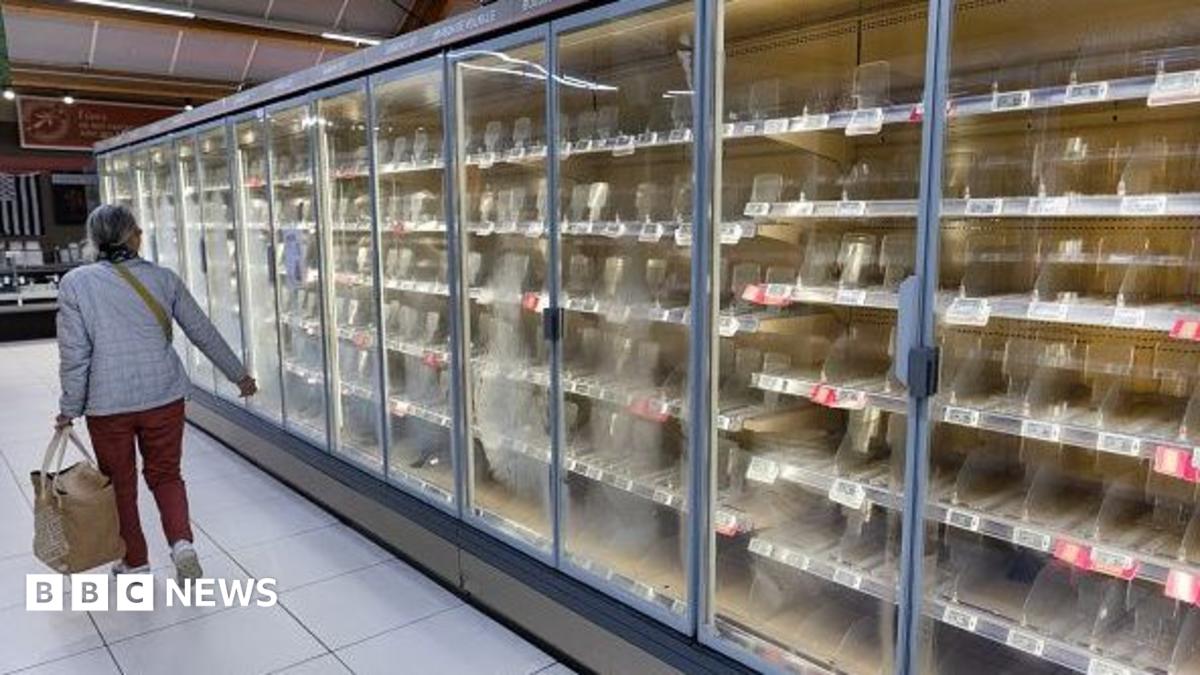
A suspected cyber-attack affecting supermarket fridges and freezers across Europe has raised questions about the security of internet-connected equipment. The incidents targeted shops in seven European countries, according to the BBC. There is no evidence that domestic appliances were targeted.
Connected devices such as fridges, heating systems and washing machines can be controlled remotely, but internet access alone does not mean attackers can easily take control. In 2015, researchers demonstrated that a vulnerability in a Samsung smart fridge could let them intercept internet traffic.
Researchers from UK Cyber Defence identified more than 800 refrigeration and building-control interfaces associated with British retailers that were accessible over the public internet. That does not mean they could be hacked, but weak passwords or software vulnerabilities could expose them to attackers. The UK's National Cyber Security Centre said it was working with international partners and industry to understand the incidents and was unaware of any impact in the UK.
Since April 2024, UK law has required manufacturers of certain consumer smart devices to meet minimum cybersecurity standards, including rules on passwords and security updates. Former NCSC chief executive Ciaran Martin said manufacturers should do more to make connected products secure. He also advised consumers to update devices and enable multi-factor authentication where possible.
Security experts warn that taking control of connected equipment can disrupt physical operations, not just computer systems. A 2015 demonstration of a remote hack of a Jeep through its internet-connected entertainment system led to improvements in vehicle security. Experts also point to risks for industrial equipment and utilities, particularly where older equipment and inconsistent security standards are involved.
Comments
0No comments yet. Be the first to comment.