

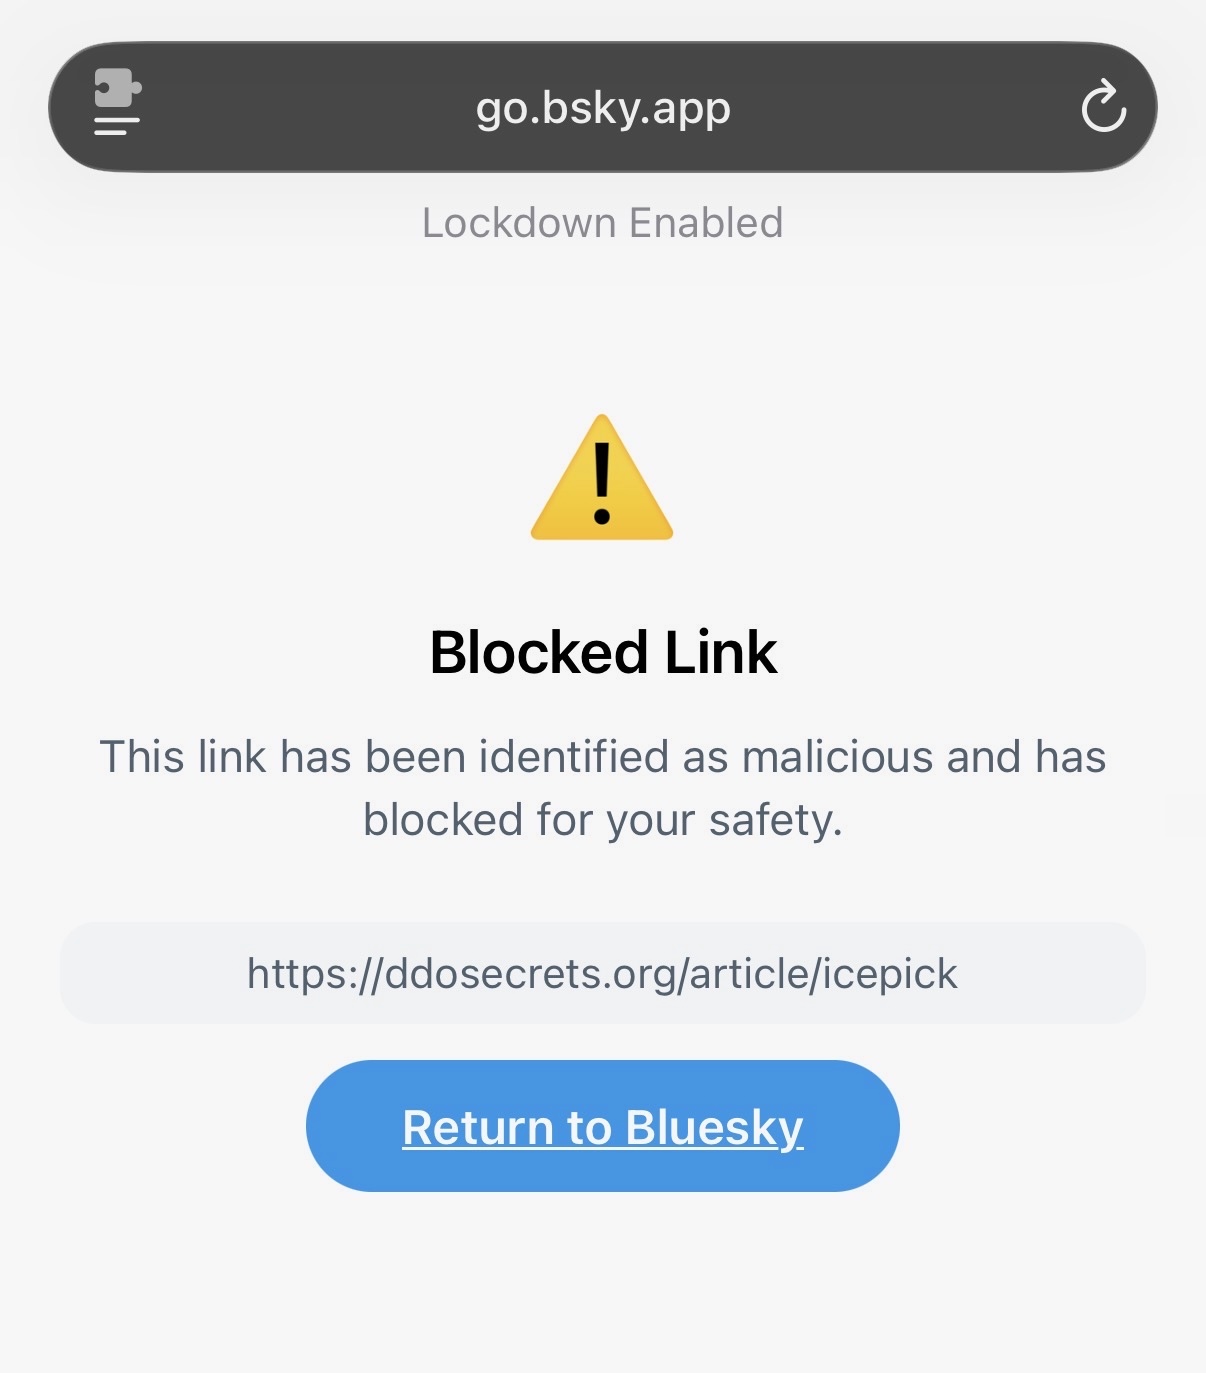
Bluesky is blocking links to a nonprofit website hosting data stolen from the U.S. Department of Homeland Security (DHS), after the social network’s users reported that the links were marked “malicious.” The move has drawn criticism because the site contains professional contact details for government employees.
TechCrunch reported that a hacker obtained more than 40,000 user account records from DHS’s login system. The records include names and work contact information, such as phone numbers and email addresses, for employees across agencies including Customs and Border Protection (CBP) and Immigration and Customs Enforcement (ICE). The data was made publicly available by DDoSecrets, a nonprofit transparency collective that publishes leaked datasets.
A DHS spokesperson told TechCrunch the department was aware of a potential breach and was working to address it. A Bluesky spokesperson told Wired that the exposed data violates the platform’s community guidelines. Bluesky blocked the links rather than removing the posts, according to TechCrunch.
DDoSecrets co-founder Emma Best told TechCrunch that the dataset does not include home addresses or personal contact information. She said professional contact details can matter to people seeking government records through public access laws.
Separately, DHS filed a takedown notice through security vendor ZeroFox, which is authorized to act on the department’s behalf until 2028. A searchable copy of the stolen data hosted by journalist maia arson crimew stopped loading, and an internet record showed the domain on “serverHold.” The domain registrar and ZeroFox did not respond to TechCrunch’s requests for comment.
Comments
0No comments yet. Be the first to comment.