

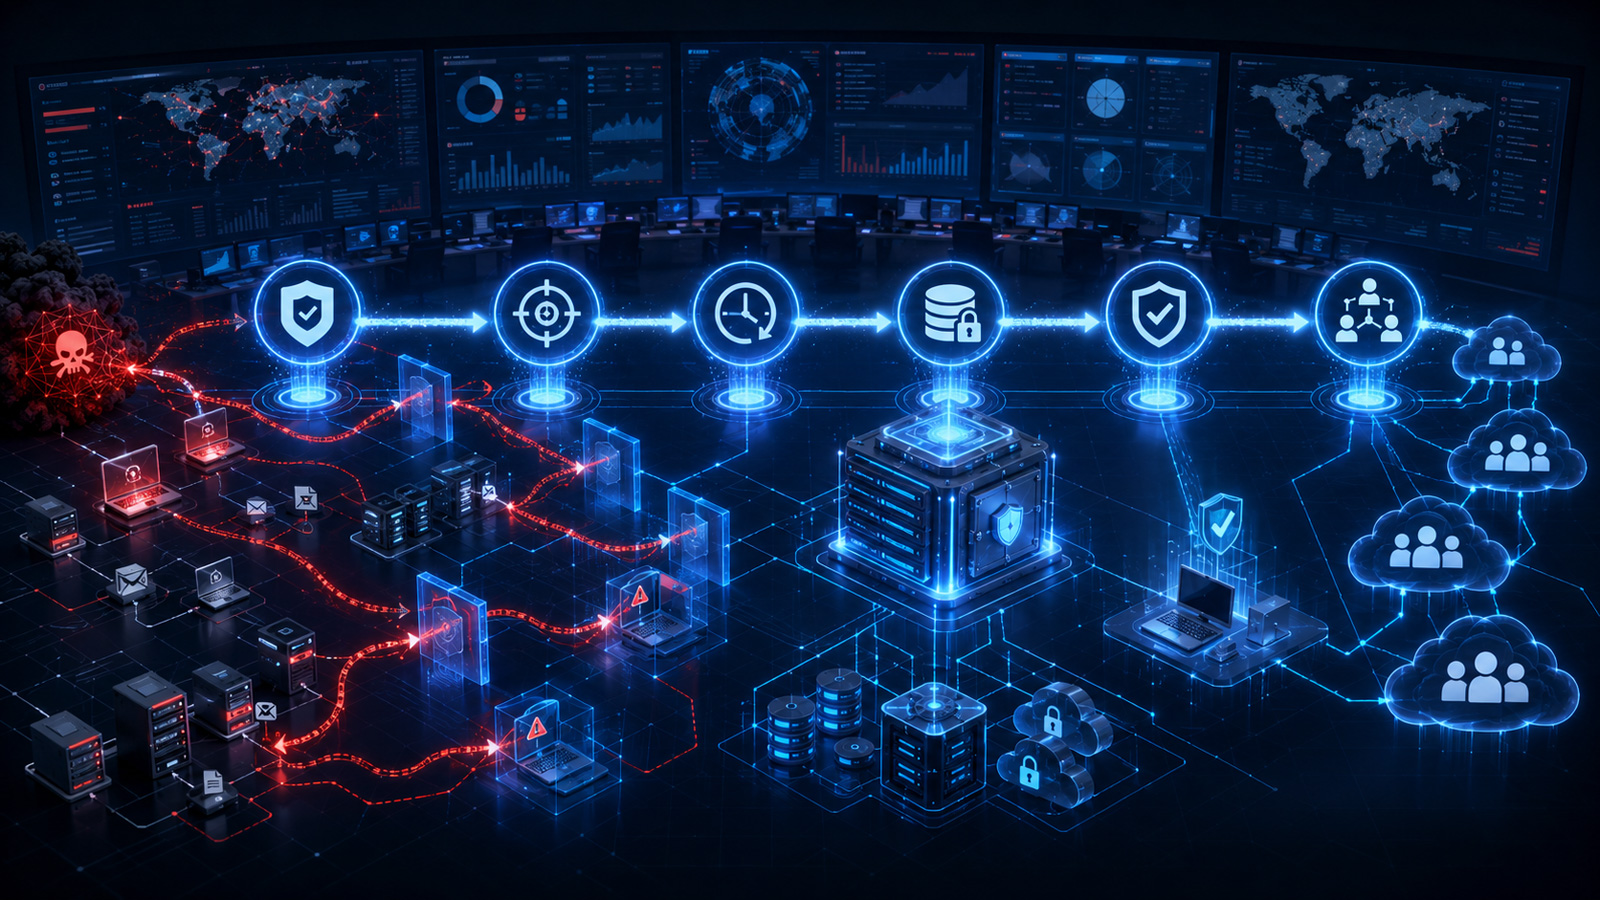
Acronis says ransomware protection for managed service providers (MSPs) should deliver six tested outcomes: reducing exposure, detecting activity before encryption, providing 24/7 response, preserving isolated recovery points, recovering cleanly, and operating consistently across tenants.
The company’s checklist follows findings from the Acronis Cyberthreats Report, which identified 143 MSP, IT-service provider and telecom ransomware victims in 2025. Phishing accounted for 52% of initial access cases, while unpatched vulnerabilities accounted for 27%.
Acronis recommends testing patch service-level agreements, multifactor authentication for management portals and remote access, separated backup and security administration, and deletion attempts using compromised credentials. It also says providers should test behavioral detection, endpoint isolation, response actions across identity, email and Microsoft 365, and after-hours escalation paths.
Acronis Cyber Protect Cloud includes vulnerability assessment, patch management, URL filtering, role-based administration, immutable backup storage, multi-tenant management, centralized reporting and RMM/PSA integrations. Acronis Active Protection and EDR cover endpoint behavior, while Acronis XDR extends visibility to email, identity and Microsoft 365. Acronis MDR provides 24/7/365 monitoring and response on top of EDR or XDR.
The checklist distinguishes immutable, offline and air-gapped copies. It also states that immutable backup protects recovery points but does not detect data theft or replace incident response. Recovery drills should record achieved recovery point objectives (RPOs) and recovery time objectives (RTOs).
Comments
0No comments yet. Be the first to comment.