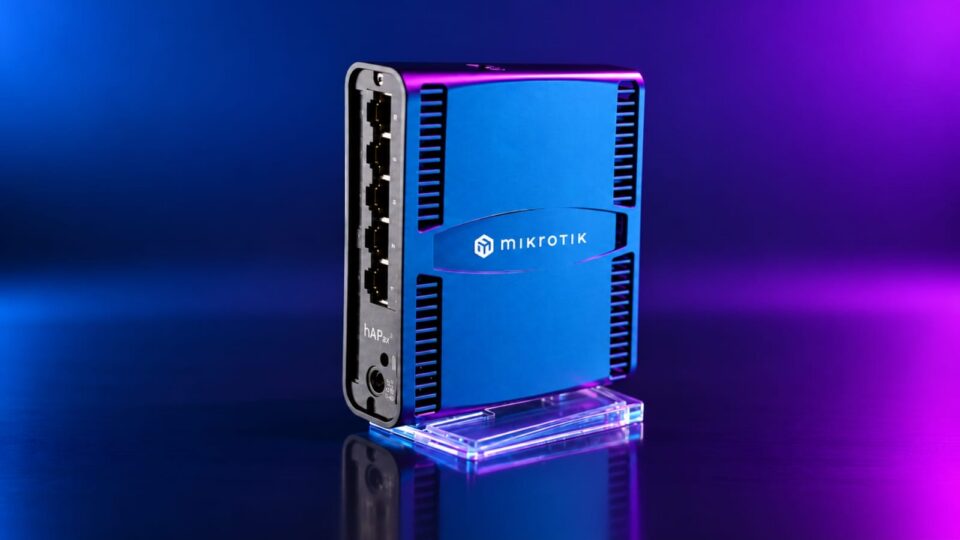
CISA warns of critical pre-authentication flaw in MikroTik RouterOS
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has warned of a critical vulnerability in MikroTik RouterOS that could allow remote code execution or cause a denial-of-service condition. Tracked as CVE-2