

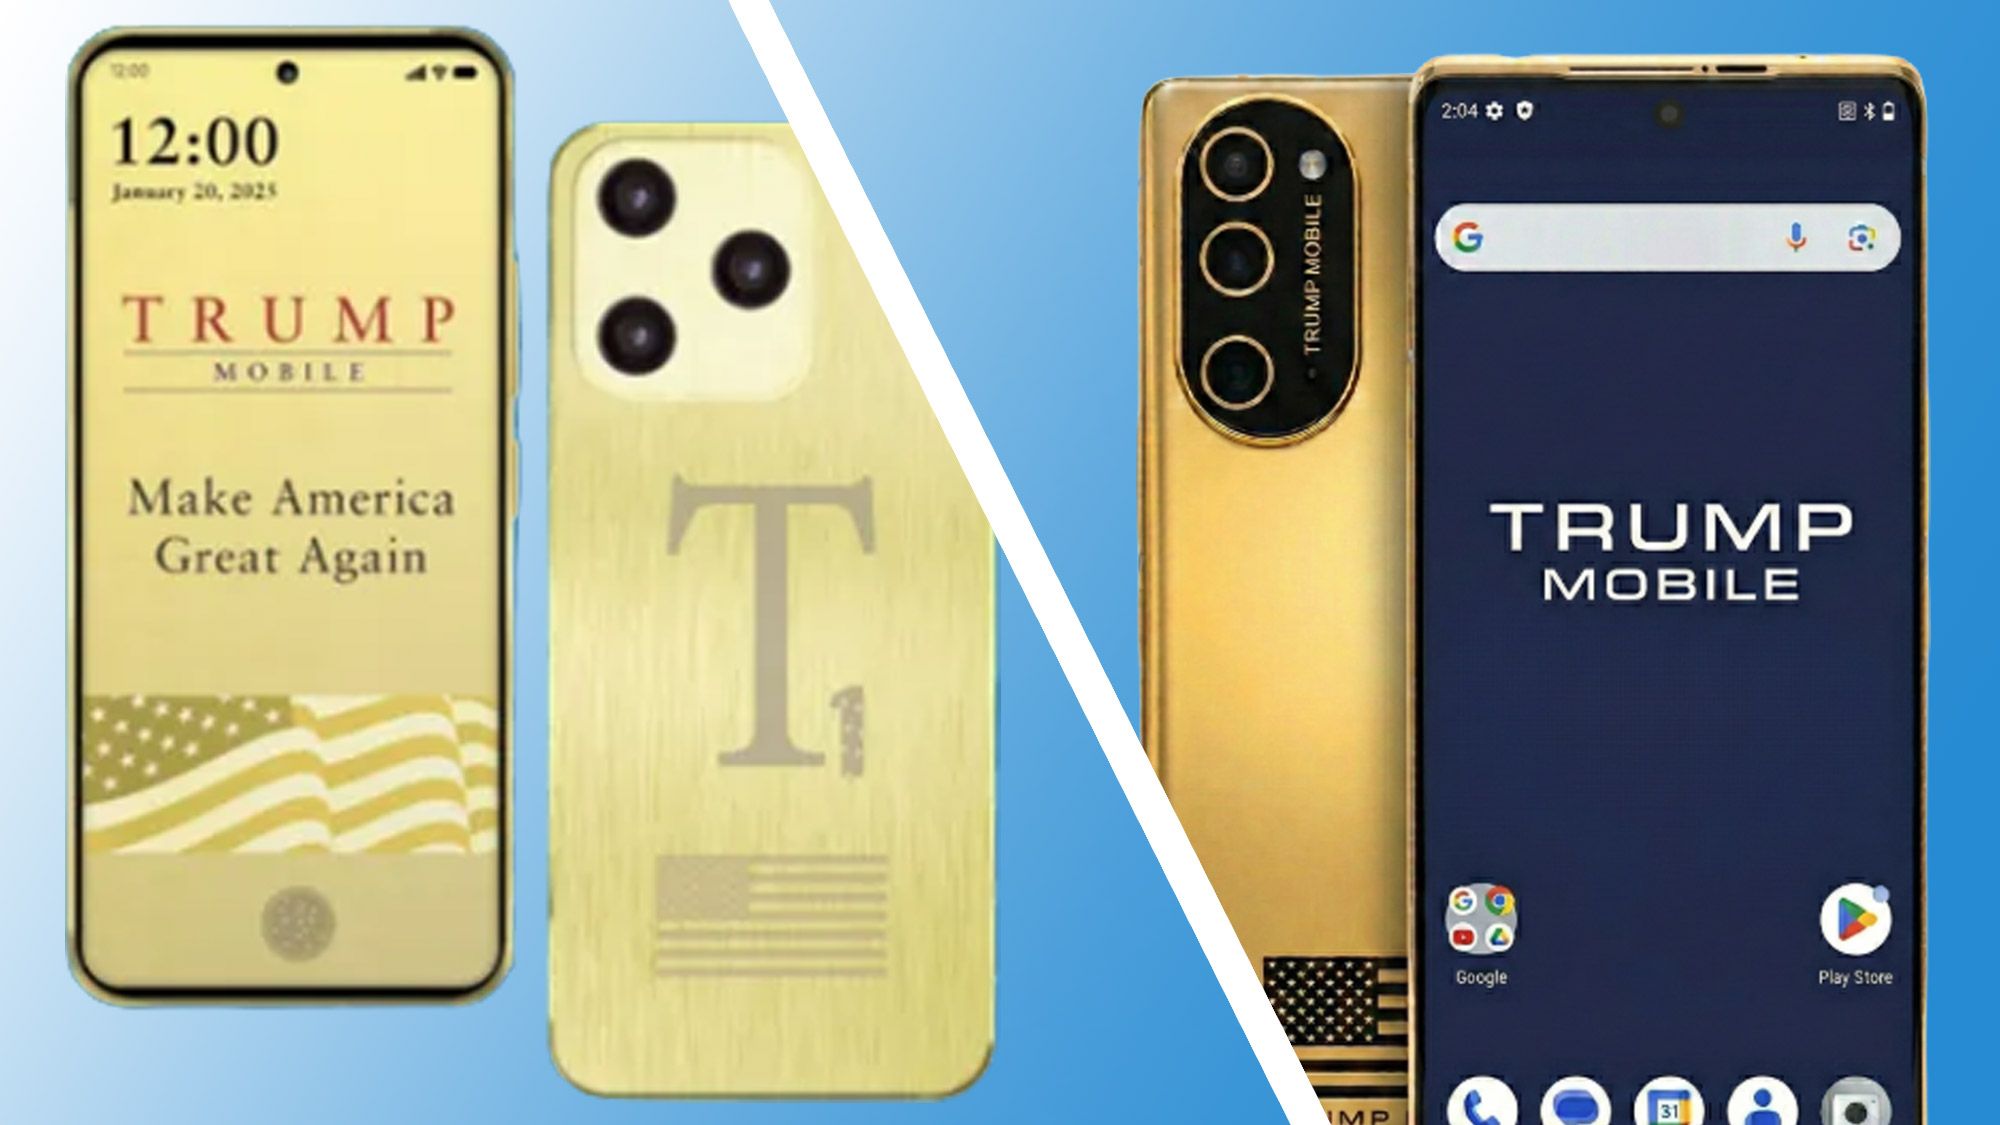
A cybercrime group calling itself BYOD claims it stole and published personal data belonging to 3,615 Trump Mobile customers. The dataset reportedly includes names, email addresses, phone numbers, home addresses and order details.
Straight Arrow News first reported the leak after reviewing the data and contacting people listed in it. Some people contacted by the outlet confirmed their details were accurate. Cybernews said its samples appeared genuine, while PCMag reported that three people it reached were listed in the file.
BYOD posted the data to its dark web leak site in late September 2026. A ransomware tracker cited by IBTimes UK dates the listing to September 29. The Register describes BYOD as a new ransomware-as-a-service operation. However, reporting cited in the source says there is no public evidence so far of encrypted systems or a ransom demand.
Accounts differ on how the group gained access: BYOD described compromising a Liberty Mobile employee with an infostealer, while other reports describe a remote access trojan. BYOD also claims it reached exposed Trump Mobile subdomains and still has access to a customer dashboard. That access has not been independently confirmed. Trump Mobile, the Trump Organization and Liberty Mobile had not responded to requests for comment cited in the reports.
No payment card data has been reported in the dataset. The source reports that Trump Mobile has not publicly commented on this incident.
Comments
0No comments yet. Be the first to comment.